
-
ceo.bfi@gmail.com
Send Email
-
2C, C-6/A Block, Janakpuri, Delhi India 110058
Visit Our Office
99902-92279
Confidentiality Guaranteed
99902-92279
Confidentiality Guaranteed
Cyber Forensic Investigation Services
-
BRILLIANT FORENSIC INVESTIGATION | Best Forensic Expert Delhi India | Handwriting Signature Verification Expert| Training Internship in forensic lab > Cyber Forensic Investigation Services

Cyber Forensic Investigation Services In India
Advanced Cyber Forensics, Digital Evidence Analysis & Cybercrime Investigation
Cybercrime is no longer limited to hacking a computer or stealing a password. Modern investigations can involve smartphones, laptops, cloud accounts, email systems, social-media platforms, messaging applications, online payments, CCTV systems, corporate networks, malware, ransomware, digital documents and large volumes of system-generated information.
Brilliant Forensic Investigation (BFI) provides Cyber Forensic Investigation Services in India for businesses, law firms, investigators, organisations and individuals dealing with suspected cybercrime, fraud, data theft, unauthorised access, ransomware, digital harassment, impersonation, intellectual-property theft, financial scams and other technology-related disputes.
Cyber forensic investigation is the systematic examination of digital systems and electronic evidence to understand what happened, when it happened, how it happened, what information was affected, what traces remain, and what evidence can be technically supported.
BFI’s current service offering already identifies digital evidence recovery, system-log analysis, network traffic examination, evidence preservation, email forensics, mobile and computer forensics, social-media investigation, financial fraud investigation, malware and ransomware investigation, data recovery, network and cloud forensics, and cyber-threat intelligence as major service areas.
A professional cyber forensic investigation does not depend on one screenshot, one IP address or one suspicious file. Stronger findings are usually developed by correlating multiple evidence sources, preserving relevant data, documenting the acquisition process, analysing technical artifacts and explaining the limitations of the available evidence.
What Is Cyber Forensic Investigation?
Cyber forensic investigation is a specialised branch of digital forensics concerned with the examination of electronic systems, digital traces and cyber-incident evidence.
The investigation can involve computers, smartphones, servers, networks, cloud platforms, email systems, applications, digital storage media, websites, databases, CCTV systems and other technology environments.
Similarly, an online fraud investigation may involve a mobile phone, WhatsApp conversations, email messages, payment records, suspicious websites and device artifacts. The value of the investigation comes from correlating the records, not simply collecting them.
BFI’s approach should therefore focus on:
Identification → Preservation → Acquisition → Examination → Analysis → Correlation → Reporting
This is consistent with established digital-forensic methodologies that separate evidence acquisition and preservation from examination, analysis and reporting. NIST SP 800-86 describes these as distinct activities within forensic incident response.
Cyber Forensics vs. Digital Forensics
Cyber forensics and digital forensics overlap considerably, but the scope can differ.
Digital forensics generally focuses on electronic evidence from devices and digital systems.
Cyber forensics often extends into incidents involving unauthorised access, cyberattacks, malware, ransomware, network intrusion, online fraud, phishing, account compromise and other technology-enabled offences.
A cyber forensic investigation can therefore include:
Computer forensics, mobile forensics, email forensics, network forensics, cloud forensics, malware analysis, digital evidence recovery, browser analysis, social-media investigation, data-breach investigation and forensic reporting.
BFI can combine these disciplines when a case spans several evidence sources.
Why Cyber Forensic Investigation Is Important in India
India’s cyber environment has expanded rapidly alongside digital payments, cloud computing, mobile applications, e-commerce and technology-driven business operations.
NCRB data for 2023 recorded 86,420 registered cybercrime cases in India, compared with 65,893 in 2022. Of the 2023 cases, 59,526 cases, or 68.9%, were recorded with fraud as the motive. The data represent registered crime and do not measure every cyber incident or attempted attack.
The economic risk associated with cyber incidents has also become significant. IBM’s 2026 India findings reported an average total organisational cost of a data breach of ₹25.5 crore, up from ₹22 crore the previous year. The same study reported an average of 39,500 records compromised and identified phishing—including voice and SMS phishing—as the most common initial attack vector in the India study.
India’s threat volume is also reflected in DSCI’s India Cyber Threat Report 2025. The report analysed 369.01 million malware detections across 8.44 million endpoints and examined threats including AI-powered malware, ransomware, supply-chain attacks, app scams and hacktivism.
The digital-forensics industry itself is expanding. Deloitte India and DSCI reported in 2025 that India’s digital-forensics market was approximately ₹1,603 crore in FY2023–24 and was projected to reach ₹11,829 crore by FY2029–30. Their analysis put mobile forensics at approximately 51% of the market and the government sector at around 81% of market demand in the reported landscape.
Government forensic capacity is expanding as well. In March 2026, the Ministry of Home Affairs stated that six additional National Cyber Forensic Laboratories were approved across CFSL locations including Delhi, Bhopal, Pune, Chandigarh, Kolkata and Kamrup, with a total financial outlay of ₹126.84 crore. The same release stated that CFSL Kolkata had handled about 794 cyber/computer forensic cases over the preceding three years.
These figures do not mean that every individual or organisation is facing the same level of risk. They show why structured cyber forensic investigation and digital evidence preservation have become increasingly important in India.
Computer Forensic Investigation Services
Computer forensics is one of the core disciplines within cyber forensic investigation because desktop computers and laptops can retain extensive traces of user and system activity. BFI can examine relevant Windows, macOS or Linux systems, subject to the nature of the device, available access and the lawful scope of the assignment. The examination can include file systems, user profiles, browser activity, downloaded files, operating-system artifacts, installed applications, temporary data, system events, removable-media history, configuration changes and other technical records that may help reconstruct what occurred.
In an employee investigation, for example, the objective may be to determine whether confidential documents were accessed, copied, archived, transferred to a USB device or synchronized to an external cloud account. In a cyberattack, the examination may focus on suspicious executables, persistence mechanisms, abnormal account activity, system changes and indicators of intrusion. The important distinction is that finding a file on a computer does not automatically prove who created, copied or transmitted it. Stronger attribution generally requires correlation with account activity, timestamps, logs, communication records and other independent evidence.
Government forensic laboratories in India identify computer forensics as an established examination area, and CFSL Bhopal publicly describes digital evidence and computer-forensic examination alongside mobile-forensic and image-processing capabilities. BFI can position its computer-forensic service around that same evidence-led principle while tailoring the depth of examination to the client’s investigative question.
Laptop and Endpoint Forensics
Corporate laptops are often the point where business communications, documents, browser activity and removable media intersect. Endpoint forensics can therefore be particularly useful in internal investigations, suspected intellectual-property theft, employee misconduct, unauthorised access, malware incidents and disputed business activity.
A detailed endpoint examination may correlate local files with operating-system records, browser artifacts, application usage, user profiles, USB activity and security telemetry. Where enterprise logging is available, local evidence can be compared with identity-provider, email, VPN, SIEM or endpoint-detection records. This can help build a chronology around a particular event rather than producing a disconnected list of artifacts.
Modern enterprise DFIR research also shows the importance of combining endpoint and mobile evidence. Magnet Forensics’ 2026 enterprise research reported that 61% of surveyed respondents said their investigations always or often require a forensic tool to collect data from mobile devices and tablets, while 66% reported that the number of mobile devices involved in investigations is growing. This makes the endpoint-plus-mobile combination increasingly relevant to corporate cases.
Mobile Phone Forensic Investigation
Smartphones have become central evidence sources because they combine communications, photographs, videos, contacts, application data, web activity, location-related artifacts and cloud connectivity in a single device. BFI can conduct Mobile Phone Forensic Investigation Services in India subject to device model, operating system, security controls, physical condition, acquisition options and lawful authority.
A forensic mobile examination can investigate relevant communications, application databases, media, browser artifacts, contacts, call-related records, documents, account information, backup traces and location-related artifacts where technically available. Government forensic sources in India identify mobile phones and related storage media as dedicated digital-forensic evidence sources, while CFSL Bhopal describes the use of specialised mobile-forensic systems in its laboratory environment.
Mobile evidence can be especially important in employee investigations, financial fraud, cyber harassment, impersonation, extortion, online scams and cases involving communication through applications that may not be visible from company infrastructure.
At the same time, mobile forensics has technical limits. Encryption, device security, operating-system changes, factory resets, data overwriting and application retention behaviour can affect what can be recovered. BFI should therefore describe the service in terms of forensic examination and technically feasible recovery, rather than guaranteeing access to every item stored on a phone.
Digital Evidence Identification, Acquisition and Preservation
Cyber forensic investigation begins before analysis. The first task is determining which electronic sources may contain evidence relevant to the incident and which sources are most likely to answer the investigative questions.
The source universe can include computers, smartphones, servers, external drives, USB devices, memory cards, cloud accounts, enterprise email, messaging applications, network logs, CCTV systems, virtual machines, databases and other connected technology. India’s official cyber-forensic ecosystem reflects the breadth of this evidence environment. CFSL Guwahati lists digital storage media, mobile devices, DVR/drone/spy cameras, email, social-media applications and internet artifacts among its examination areas, while Maharashtra DFSL describes evidence acquisition and analysis across computers, mobile devices, servers, DVR/CCTV and cloud platforms.
Acquisition should be designed to preserve the evidentiary characteristics of the source. Depending on the case, this may involve forensic imaging, controlled extraction, hash verification, acquisition notes, evidence identification and chain-of-custody records. ISO/IEC 27037 specifically addresses the identification, collection, acquisition and preservation of potential digital evidence.
Forensic Imaging and Digital Evidence Preservation
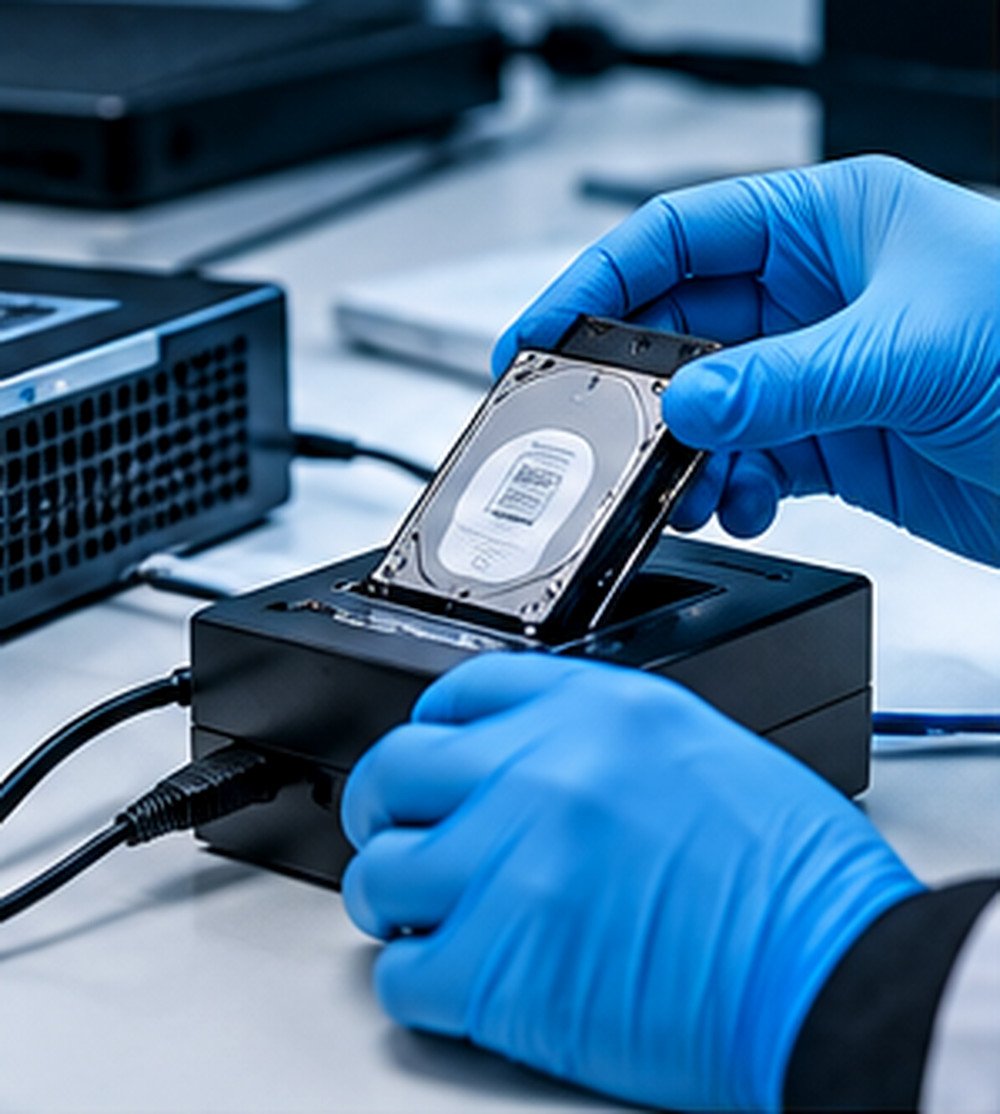
Forensic imaging is the creation of a controlled forensic copy of relevant digital media so that examination can be performed against the acquired data rather than repeatedly interacting with the original source. In a serious investigation, acquisition details should be recorded along with the identity and condition of the source and the process used to create the forensic copy.
The integrity component is particularly important because digital evidence can change as a result of ordinary device activity. Hash values are therefore commonly used to document the integrity of digital objects or forensic images. The Bharatiya Sakshya Adhiniyam, 2023 Schedule specifically includes device/source categories such as computer or storage media, DVR, mobile, flash drive, server and cloud and provides fields for hash values, including SHA1 and SHA256.
For BFI, the strongest website positioning is to explain that forensic imaging supports a controlled examination process, helps preserve integrity and creates a documented technical record. It should not be marketed as a universal guarantee of court admissibility.
Deleted Data Recovery and Digital Data Recovery
Deleted digital information can sometimes remain partially or fully recoverable, depending on how the deletion occurred and what happened to the underlying storage afterwards. BFI can examine relevant file-system structures, unallocated areas, application databases, temporary storage, caches, thumbnails, backups and other residual artifacts when technically appropriate.
Recovery results can range from complete files to fragments, metadata-only records or database references. In some cases, information may be impossible to recover because it has been overwritten, encrypted or securely erased. Solid-state storage, mobile operating systems and modern security features can further reduce recoverability.
This is why professional deleted data recovery services in India should begin with examination rather than a blanket recovery promise. The final report should make it clear whether the information was fully recovered, partially recovered, reconstructed from residual artifacts, identified only through metadata, or not recovered at all.
WhatsApp, Chat and Messaging Forensics
Messaging applications can become critical evidence in cybercrime, fraud, harassment, extortion, employee investigations and disputes involving digital communications. BFI can examine relevant messaging evidence where the source can be lawfully obtained and technically examined.
The examination may involve application databases, message content, attachments, photographs, videos, participant information, timestamps and related device artifacts. Depending on the application and device, the examiner may also be able to correlate messages with local file activity, notifications, backups or other system records.
A screenshot alone may not preserve all of the relevant context. The Government of India’s National Cyber Crime Reporting Portal itself identifies chat transcripts, email copies, URLs, suspect phone-number screenshots, videos, images and other documents as potentially relevant evidence for cybercrime complaints. BFI’s service can therefore focus on preserving and analysing the underlying digital evidence rather than treating a screenshot as the complete investigative record.
Social Media Forensic Investigation
Social-media platforms can generate evidence concerning impersonation, harassment, fraud, extortion, threats, identity misuse, reputational attacks and online interactions. BFI’s Social Media Forensic Investigation Services can focus on preserving relevant information and correlating public or lawfully obtained evidence with other digital sources.
A professional social-media forensic examination can consider profile information, account identifiers, URLs, public posts, media, interactions, messages where lawfully accessible, chronology and other technical or contextual indicators. The goal is to understand the evidence trail rather than simply archive screenshots.
The Government of India’s suspect-reporting facility specifically permits reporting suspicious website URLs, WhatsApp numbers, Telegram handles, phone numbers, email IDs, SMS headers/numbers and social-media URLs, with supporting evidence upload. This illustrates the increasingly interconnected nature of online identities across platforms.
Attribution should remain evidence-based. The existence of a fake social profile is an investigative lead; it does not, by itself, prove the identity of the person operating the account.
Email Forensic Investigation
Email evidence can provide important technical information in phishing, business-email compromise, account takeover, impersonation, fraudulent invoice cases and corporate disputes. BFI can conduct Email Forensic Investigation Services focused on the original message, headers, routing information, authentication indicators, timestamps, attachments and related mailbox or endpoint evidence where available.
A forensic email investigation should distinguish the visible sender address from the technical path of the message. Header analysis can help assess routing and authentication characteristics, while enterprise mail logs and identity systems may provide additional context about account use.
The investigation becomes stronger when email evidence is correlated with other digital sources. For example, a suspicious invoice may be linked to a mailbox event, a login from a particular device, a newly created domain or a corresponding chat communication. BFI can reconstruct these relationships while clearly distinguishing confirmed findings from investigative hypotheses.
Email Spoofing, Phishing and Business Email Compromise Investigation
Phishing and email spoofing investigations often involve a combination of email artifacts, websites, domains, browser activity, endpoint evidence and account logs.
A suspicious email can contain a deceptive sender identity while the underlying headers reveal a different technical path. BFI can analyse the available information to determine whether the message shows characteristics consistent with spoofing, phishing or account compromise.
CERT-In continues to operate the official cyber-incident framework under Section 70B of the Information Technology Act, 2000, and its materials distinguish specified cyber incidents and data breaches that require reporting within the applicable framework. For a private forensic investigation, this does not replace an organisation’s reporting obligations; rather, it reinforces the importance of preserving the technical evidence needed to understand the incident.
Cloud Forensic Investigation
Cloud systems have fundamentally changed where digital evidence resides. Relevant information may be distributed across cloud storage, enterprise email, identity providers, collaboration applications, SaaS platforms, backups and endpoint synchronisation.
BFI’s Cloud Forensic Investigation Services in India can examine lawfully accessible cloud evidence and correlate it with endpoint and enterprise records. Potential evidence can include file activity, access records, login events, sharing histories, version records, administrative changes, mailbox activity, cloud audit information and synchronized local artifacts.
Current forensic technology providers increasingly treat cloud evidence as a normal component of digital investigations rather than a separate niche. Cellebrite’s enterprise platform describes evidence collection across mobile, computer and cloud environments, while Magnet Forensics similarly integrates mobile, cloud and computer data into unified investigative workflows.
Cloud retention can be a limiting factor. Some records may be unavailable after provider retention periods expire, making timely preservation particularly important.
Network Forensics and Log Analysis
Network forensics examines digital traffic and system activity to reconstruct what happened during a cyber incident. BFI can analyse relevant firewall, VPN, DNS, proxy, authentication, mail-server, web-server, SIEM and endpoint records where those logs are available.
Network evidence can be particularly useful in intrusion, malware, ransomware, account compromise and data-exfiltration investigations. The objective may be to identify the sequence of events, locate suspicious connections, establish the time of access and correlate network activity with endpoint or user activity.
CERT-In’s official FAQ identifies firewall, intrusion-prevention, SIEM, web-server, database-server, mail-server, proxy, SSH and VPN logs among examples of ICT logs relevant to cyber-incident analysis. The actual evidence set depends on the organisation’s architecture.
Server Forensic Investigation
Servers can contain evidence that does not exist on end-user devices. A server investigation may examine authentication records, application logs, configuration changes, access histories, scheduled tasks, files, databases, web activity and other technical artifacts.
In a corporate breach, the server examination can help determine whether an account was used to access restricted systems, whether files were copied, whether malicious code was introduced or whether privileged access changed before or after the incident.
Server forensics is often most valuable when correlated with network and endpoint evidence. An authentication event on a server, for example, may become more meaningful when the corresponding VPN session, endpoint artifact and user account activity can be aligned in a common chronology.
Malware Forensic Investigation
Malware forensics examines malicious software and the traces it leaves across devices and networks. BFI can investigate suspicious files, execution artifacts, persistence mechanisms, affected accounts, system changes, network indicators and other evidence relevant to an infection.
The investigation can address questions such as how the malware entered the environment, which system was first affected, what executed, whether persistence was established, what systems were touched and whether information may have been staged or transferred.
The India Cyber Threat Report 2025 analysed 369.01 million malware detections across 8.44 million endpoints in its telemetry study and reported that Trojans and infectors accounted for 68% of attacks in its detection breakdown. These numbers are telemetry findings, not a measure of every cyber incident in India, but they demonstrate the scale of malware-related activity that forensic investigators may encounter.
Ransomware Forensic Investigation
Ransomware investigations require more than confirming that files have been encrypted. The forensic questions often concern initial access, execution, persistence, account activity, lateral movement, affected systems, data staging and potential exfiltration.
CERT-In’s India Ransomware Report 2024 identified LockBit, RansomHub and KillSec among the dominant ransomware groups affecting Indian cyberspace during 2024 and described changing tactics, variants and affiliate structures. CERT-In also publishes ransomware alerts describing techniques such as exploitation of exposed services and malicious email attachments.
BFI can support ransomware investigations by preserving affected systems and analysing relevant endpoint, server, network and log evidence. In a live incident, forensic investigation should be coordinated with containment, recovery, legal and regulatory stakeholders rather than performed in isolation.
Data Breach Forensic Investigation
A data breach investigation seeks to determine what happened to information, systems or accounts and to reconstruct the relevant incident timeline. The investigation can examine the systems that were accessed, accounts that were used, suspicious activity, files or databases involved and indicators of data movement.
IBM’s 2026 India study reported an average total cost of a data breach of ₹25.5 crore and an average of 39,500 records compromised in its India study. It also reported that phishing, including voice and SMS phishing, was the most common initial attack vector in India and that 26% of malicious breaches in its India study were AI-generated.
BFI’s role in a breach investigation should be presented as forensic reconstruction and evidence analysis. It can help determine what the technical evidence supports, but notification, regulatory reporting, legal assessment and public communications remain separate responsibilities for the affected organisation and its advisers.
Financial Cyber Fraud Investigation
Digital payment fraud can generate evidence across phones, chats, emails, bank communications, payment references, websites and accounts. BFI can investigate the digital side of these cases by examining available devices and correlating the electronic evidence with transaction information supplied by the client or relevant institution.
A financial-fraud chronology may connect a suspicious message to a website, account login, payment instruction, UPI reference and subsequent communication. The value of forensic analysis lies in establishing these relationships and documenting the underlying evidence.
The National Cyber Crime Reporting Portal instructs complainants to keep incident date and time, financial transaction information, relevant evidence, suspected websites or social-media handles and other available identifying information. For financial fraud, the portal specifically asks for information such as bank or wallet details, transaction/UTR number, transaction date and fraud amount.
Victims of cyber-financial fraud should use the official reporting channels immediately. The Government portal states that 1930 is available for immediate reporting of cyber-financial fraud. Private forensic analysis can supplement, but does not replace, those official reporting processes.
Online Scam and Digital Fraud Investigation
Online scams frequently involve multiple digital identities rather than one obvious source. A fraudulent seller, investment scam, impersonation scheme or payment scam can leave traces across websites, social-media accounts, email, messaging applications, phone records and transaction records.
BFI can investigate these digital trails and organise the evidence into a structured chronology. Relevant findings may include relationships between websites, identities, communications and payment instructions, subject to lawful access and available evidence.
Because online fraudsters may use compromised accounts, temporary numbers and spoofed websites, attribution requires caution. Digital investigation should identify what can be technically established rather than turning a suspicious association into an unsupported allegation.
Cyber Harassment, Cyberstalking and Online Impersonation Investigation
Digital harassment and impersonation can involve persistent messages, fake accounts, copied images, spoofed email addresses, fraudulent websites and other forms of identity misuse.
BFI can preserve available digital information and examine the relationship between messages, profiles, devices, accounts, URLs and other relevant evidence. Public-source captures should preserve the source location, date and context so that the evidence can later be understood rather than viewed as an isolated screenshot.
The Government’s National Cyber Crime Reporting Portal explicitly supports reporting of suspicious website URLs, WhatsApp numbers, Telegram handles, phone numbers, email IDs, SMS headers and social-media URLs.
Where the identity of an anonymous operator is at issue, additional evidence or provider-held information may be necessary. Publicly visible content alone may not establish the underlying person’s identity.
Intellectual Property Theft and Corporate Data Leakage Investigation
Corporate data theft can involve source code, customer lists, contracts, pricing information, product documents, designs, research files or internal reports. BFI can investigate digital indicators of access and movement of such information.
The forensic examination may correlate file-access history, removable-media activity, cloud synchronization, email attachments, archive creation, downloads and account events.
This kind of investigation is especially relevant when an employee leaves an organisation and there is concern that confidential information may have been copied. Magnet Forensics’ enterprise research specifically identifies data exfiltration and intellectual-property theft as common enterprise investigation scenarios and notes the growing importance of mobile devices in such matters.
The investigation should distinguish access from transfer. A person opening a confidential document does not automatically prove that the document was disclosed externally; additional evidence may be necessary to establish copying or transmission.
Employee and Insider Threat Digital Investigation
Insider investigations may arise from suspected data theft, misuse of company systems, unauthorised access, policy violations, fraud or disclosure of confidential information.
A defensible corporate investigation begins by defining the organisation’s authority and scope. The relevant laptop, mobile device, company email, cloud account, access logs and other systems should be identified before acquisition begins.
Mobile evidence is increasingly relevant because employees may use personal devices for corporate messaging and cloud access. Magnet’s 2026 enterprise DFIR research reported continued growth in mobile-device involvement and noted encryption, device security and privacy requirements as important factors affecting investigative workflows.
Where a Bring Your Own Device environment is involved, the scope of collection should be tightly defined to avoid unnecessary acquisition of unrelated personal information.
Browser and Internet Forensics
Web browsers can retain evidence of online activity through history, downloads, cookies, cache, search records, session information, extensions and application-related artifacts.
BFI can examine browser evidence when investigating cyber fraud, phishing, malware, unauthorised access, online harassment, suspicious downloads or employee activity.
Browser artifacts should be interpreted carefully. An access record may show that a device interacted with a website, but it does not automatically establish who was physically operating the system at that moment. Correlation with account activity, endpoint evidence, network records and other artifacts can strengthen the chronology.
CCTV, DVR and NVR Forensic Investigation
CCTV systems can become important evidence in cyber and broader digital investigations. BFI can examine CCTV footage, DVR/NVR exports and related digital records where technically and lawfully available.
The investigation can assess chronology, relevant events, camera sequences, timestamp consistency, export characteristics, recording gaps and image quality. Where access to the original recorder is possible, source-level examination may provide more information than a short exported clip.
Government forensic resources in India explicitly recognise DVR/CCTV examination as part of cyber-forensic capability. Maharashtra DFSL lists DVR/CCTV within its digital-evidence scope, while CFSL Guwahati lists DVR and other camera sources among its digital-forensic evidence types.
Video enhancement can improve visibility or intelligibility, but it cannot reliably create details that were never captured by the original recording.
Audio and Video Forensic Investigation
Audio and video files may contain evidence relevant to fraud, threats, harassment, business disputes, cyber incidents and legal proceedings. BFI can examine the digital characteristics of recordings where the investigative question concerns authenticity, processing, chronology, enhancement or intelligibility.
Audio work may include format and metadata assessment, waveform and spectral examination, noise reduction or enhancement and synchronisation. Video examination may involve frame analysis, chronology, source characteristics and relevant-event extraction.
Any conclusion must account for compression, re-encoding, editing and recording quality. Enhancement is not the same as reconstruction of missing information, and a technically processed file should be clearly distinguished from the original source.
Hash Values and Digital Evidence Integrity
Cryptographic hashes are commonly used to document the integrity of forensic images and digital objects.
A hash provides an integrity check that can be recalculated during verification.
The current Bharatiya Sakshya Adhiniyam’s electronic-record framework includes hash-value fields in its Schedule certificate format. The Schedule specifically identifies sources such as computers, storage media, DVRs, mobiles, servers and cloud systems and provides for recording hash values.
Hashing is an integrity-control mechanism; it should not be marketed as a guarantee that a court will automatically admit the evidence.
Cyber Forensics and the Bharatiya Sakshya Adhiniyam, 2023
India’s current evidentiary framework for electronic and digital records is particularly important for forensic practitioners and lawyers.
The Bharatiya Sakshya Adhiniyam, 2023 came into force on 1 July 2024.
Section 61 addresses electronic or digital records and provides that their admissibility is not to be denied simply because they are electronic or digital records, subject to Section 63.
Section 62 addresses proof of the contents of electronic records.
Section 63 deals with admissibility of electronic records and computer output and includes a certificate mechanism in specified circumstances. The statutory Schedule provides detailed information fields for the device or source and relevant hash values.
For BFI’s website, the correct message is therefore not “every forensic report is automatically court admissible.”
A more defensible formulation is:
BFI prepares technical forensic reports with documented evidence sources, methodology, integrity information and limitations for use in legal and investigative contexts, subject to the applicable law and judicial requirements.
Why Choose Brilliant Forensic Investigation for Cyber Forensics?
BFI’s current website already positions the organisation around cyber forensic investigation, digital forensics, mobile and computer forensics, data recovery, email investigation, network analysis and related forensic capabilities.
For the national service page, BFI should differentiate its offering around:
Evidence-focused investigation
Structured forensic methodology
Digital evidence preservation
Technical analysis
Multi-source correlation
Confidential handling
Clear forensic reporting
Legal and investigative support
Where an investigation involves multiple evidence types, digital forensics can also be coordinated with BFI’s document, signature, audio-video, corporate investigation and broader forensic capabilities.
The most credible positioning is not a promise of guaranteed recovery or automatic court acceptance. It is a carefully documented forensic process designed to reduce uncertainty and explain what the available evidence supports.
Request Confidential Cyber Forensic Investigation Services in India
If a cyber incident, dispute, fraud investigation or legal matter depends on electronic evidence, early preservation and systematic forensic examination can be important.
BFI can assist with investigations involving computers, laptops, mobile phones, WhatsApp, email, social media, cloud systems, servers, networks, malware, ransomware, data breaches, online fraud, employee misconduct, intellectual-property theft, CCTV, digital documents and forensic reporting.
Brilliant Forensic Investigation provides cyber-forensic investigation support in India based on the scope, evidence sources and investigative questions relevant to each case.
Call To Action
BFI can structure the investigation around the evidence sources and questions relevant to your case.
📞 Contact Us: 9990292279
🌐 Visit Our Website: https://forensicexpertinvestigation.com/
✉️ Email: ceo.bfi@gmail.com
Frequently Asked Questions About Cyber Forensic Investigation Services
-
What is cyber forensic investigation?
Cyber forensic investigation is the scientific and technical examination of digital systems and electronic evidence to reconstruct cyber incidents, identify relevant artifacts, determine timelines and document findings.
-
What is the difference between cyber forensics and digital forensics?
Digital forensics is the broader discipline involving electronic evidence. Cyber forensics commonly focuses more specifically on cybercrime, hacking, malware, ransomware, unauthorised access, online fraud and cyber incidents.
-
What devices can BFI investigate?
Depending on the assignment, BFI can investigate computers, laptops, smartphones, tablets, hard drives, SSDs, USB devices, servers, cloud systems, CCTV/DVR/NVR systems and other digital sources.
-
Can BFI recover deleted files?
Deleted information may sometimes be recovered depending on the device, storage system, encryption, overwrite activity and other technical factors. Recovery is not guaranteed.
-
Can BFI recover deleted WhatsApp messages?
Some residual application data may be recoverable depending on the device, operating system, backups and acquisition conditions. A forensic examination is required to determine what remains.
Cyber Forensic Expert Services in India
union territory Cyber-Forensic-Investigation-Services in Andaman and Nicobar Islands (union territory)-Port Blair | Cyber-Forensic-Investigation-Services in Andhra Pradesh – Adoni, Amaravati, Anantapur, Chandragiri, Chittoor, Dowlaiswaram, Eluru, Guntur, Kadapa, Kakinada, Kurnool, Machilipatnam, Nagarjunakoṇḍa, Rajahmundry, Srikakulam, Tirupati, Vijayawada, Visakhapatnam, Vizianagaram, Yemmiganur | Cyber-Forensic-Investigation-Services in Arunachal Pradesh – Itanagar | Cyber-Forensic-Investigation-Services in Assam – Dhuburi, Dibrugarh, Dispur, Guwahati, Jorhat, Nagaon, Sivasagar, Silchar, Tezpur, Tinsukia | Cyber-Forensic-Investigation-Services in Bihar – Ara, Barauni, Begusarai, Bettiah, Bhagalpur, Bihar Sharif, Bodh Gaya, Buxar, Chapra, Darbhanga, Dehri, Dinapur Nizamat, Gaya, Hajipur, Jamalpur, Katihar, Madhubani, Motihari, Munger, Muzaffarpur, Patna, Purnia, Pusa, Saharsa, Samastipur, Sasaram, Sitamarhi, Siwan | Cyber-Forensic-Investigation-Services in Chandigarh (union territory) – Chandigarh | Cyber-Forensic-Investigation-Services in Chhattisgarh – Ambikapur, Bhilai, Bilaspur, Dhamtari, Durg, Jagdalpur, Raipur, Rajnandgaon | Cyber-Forensic-Investigation-Services in Dadra and Nagar Haveli and Daman and Diu (union territory) – Daman, Diu, Silvassa | Cyber-Forensic-Investigation-Services in Delhi (national capital territory) – Delhi, New Delhi | Cyber-Forensic-Investigation-Services in Goa – Madgaon, Panaji | Cyber-Forensic-Investigation-Services in Gujarat – Ahmadabad, Amreli, Bharuch, Bhavnagar, Bhuj, Dwarka, Gandhinagar, Godhra, Jamnagar, Junagadh, Kandla, Khambhat, Kheda, Mahesana, Morbi, Nadiad, Navsari, Okha, Palanpur, Patan, Porbandar, Rajkot, Surat, Surendranagar, Valsad, Veraval | Cyber-Forensic-Investigation-Services in Haryana – Ambala, Bhiwani, Chandigarh, Faridabad, Firozpur Jhirka, Gurugram, Hansi, Hisar, Jind, Kaithal, Karnal, Kurukshetra, Panipat, Pehowa, Rewari, Rohtak, Sirsa, Sonipat | Cyber-Forensic-Investigation-Services in Himachal Pradesh – Bilaspur, Chamba, Dalhousie, Dharmshala, Hamirpur, Kangra, Kullu, Mandi, Nahan, Shimla, Una | Cyber-Forensic-Investigation-Services in Jammu and Kashmir (union territory) – Anantnag, Baramula, Doda, Gulmarg, Jammu, Kathua, Punch, Rajouri, Srinagar, Udhampur | Cyber-Forensic-Investigation-Services in Jharkhand – Bokaro, Chaibasa, Deoghar, Dhanbad, Dumka, Giridih, Hazaribag, Jamshedpur, Jharia, Rajmahal, Ranchi, Saraikela | Cyber-Forensic-Investigation-Services in Karnataka – Badami, Ballari, Bengaluru, Belagavi, Bhadravati, Bidar, Chikkamagaluru, Chitradurga, Davangere, Halebid, Hassan, Hubballi-Dharwad, Kalaburagi, Kolar, Madikeri, Mandya, Mangaluru, Mysuru, Raichur, Shivamogga, Shravanabelagola, Shrirangapattana, Tumakuru, Vijayapura | Cyber-Forensic-Investigation-Services in Kerala – Alappuzha, Vatakara, Idukki, Kannur, Kochi, Kollam, Kottayam, Kozhikode, Mattancheri, Palakkad, Thalassery, Thiruvananthapuram, Thrissur | Cyber-Forensic-Investigation-Services in Ladakh (union territory) – Kargil, Leh | Cyber-Forensic-Investigation-Services in Madhya Pradesh – Balaghat, Barwani, Betul, Bharhut, Bhind, Bhojpur, Bhopal, Burhanpur, Chhatarpur, Chhindwara, Damoh, Datia, Dewas, Dhar, Dr. Ambedkar Nagar (Mhow), Guna, Gwalior, Hoshangabad, Indore, Itarsi, Jabalpur, Jhabua, Khajuraho, Khandwa, Khargone, Maheshwar, Mandla, Mandsaur, Morena, Murwara, Narsimhapur, Narsinghgarh, Narwar, Neemuch, Nowgong, Orchha, Panna, Raisen, Rajgarh, Ratlam, Rewa, Sagar, Sarangpur, Satna, Sehore, Seoni, Shahdol, Shajapur, Sheopur, Shivpuri, Ujjain, Vidisha | Cyber-Forensic-Investigation-Services in Maharashtra – Ahmadnagar, Akola, Amravati, Aurangabad, Bhandara, Bhusawal, Bid, Buldhana, Chandrapur, Daulatabad, Dhule, Jalgaon, Kalyan, Karli, Kolhapur, Mahabaleshwar, Malegaon, Matheran, Mumbai, Nagpur, Nanded, Nashik, Osmanabad, Pandharpur, Parbhani, Pune, Ratnagiri, Sangli, Satara, Sevagram, Solapur, Thane, Ulhasnagar, Vasai-Virar, Wardha, Yavatmal | Cyber-Forensic-Investigation-Services in Manipur – Imphal | Cyber-Forensic-Investigation-Services in Meghalaya – Cherrapunji, Shillong | Cyber-Forensic-Investigation-Services in Mizoram – Aizawl, Lunglei | Cyber-Forensic-Investigation-Services in Nagaland – Kohima, Mon, Phek, Wokha, Zunheboto | Cyber-Forensic-Investigation-Services in Odisha – Balangir, Baleshwar, Baripada, Bhubaneshwar, Brahmapur, Cuttack, Dhenkanal, Kendujhar, Konark, Koraput, Paradip, Phulabani, Puri, Sambalpur, Udayagiri | Cyber-Forensic-Investigation-Services in Puducherry (union territory) – Karaikal, Mahe, Puducherry, Yanam | Cyber-Forensic-Investigation-Services in Punjab – Amritsar, Batala, Chandigarh, Faridkot, Firozpur, Gurdaspur, Hoshiarpur, Jalandhar, Kapurthala, Ludhiana, Nabha, Patiala, Rupnagar, Sangrur | Cyber-Forensic-Investigation-Services in Rajasthan – Abu, Ajmer, Alwar, Amer, Barmer, Beawar, Bharatpur, Bhilwara, Bikaner, Bundi, Chittaurgarh, Churu, Dhaulpur, Dungarpur, Ganganagar, Hanumangarh, Jaipur, Jaisalmer, Jalor, Jhalawar, Jhunjhunu, Jodhpur, Kishangarh, Kota, Merta, Nagaur, Nathdwara, Pali, Phalodi, Pushkar, Sawai Madhopur, Shahpura, Sikar, Sirohi, Tonk, Udaipur | Cyber-Forensic-Investigation-Services in Sikkim – Gangtok, Gyalshing, Lachung, Mangan | Cyber-Forensic-Investigation-Services in Tamil Nadu – Arcot, Chengalpattu, Chennai, Chidambaram, Coimbatore, Cuddalore, Dharmapuri, Dindigul, Erode, Kanchipuram, Kanniyakumari, Kodaikanal, Kumbakonam, Madurai, Mamallapuram, Nagappattinam, Nagercoil, Palayamkottai, Pudukkottai, Rajapalayam, Ramanathapuram, Salem, Thanjavur, Tiruchchirappalli, Tirunelveli, Tiruppur, Thoothukudi, Udhagamandalam, Vellore | Cyber-Forensic-Investigation-Services in Telangana – Hyderabad, Karimnagar, Khammam, Mahbubnagar, Nizamabad, Sangareddi, Warangal | Cyber-Forensic-Investigation-Services in Tripura – Agartala | Cyber-Forensic-Investigation-Services in Uttar Pradesh – Agra, Aligarh, Amroha, Ayodhya, Azamgarh, Bahraich, Ballia, Banda, Bara Banki, Bareilly, Basti, Bijnor, Bithur, Budaun, Bulandshahr, Deoria, Etah, Etawah, Faizabad, Farrukhabad-cum-Fatehgarh, Fatehpur, Fatehpur Sikri, Ghaziabad, Ghazipur, Gonda, Gorakhpur, Hamirpur, Hardoi, Hathras, Jalaun, Jaunpur, Jhansi, Kannauj, Kanpur, Lakhimpur, Lalitpur, Lucknow, Mainpuri, Mathura, Meerut, Mirzapur-Vindhyachal, Moradabad, Muzaffarnagar, Partapgarh, Pilibhit, Prayagraj, Rae Bareli, Rampur, Saharanpur, Sambhal, Shahjahanpur, Sitapur, Sultanpur, Tehri, Varanasi | Cyber-Forensic-Investigation-Services in Uttarakhand – Almora, Dehra Dun, Haridwar, Mussoorie, Nainital, Pithoragarh | Cyber-Forensic-Investigation-Services in West Bengal – Alipore, Alipur Duar, Asansol, Baharampur, Bally, Balurghat, Bankura, Baranagar, Barasat, Barrackpore, Basirhat, Bhatpara, Bishnupur, Budge Budge, Burdwan, Chandernagore, Darjeeling, Diamond Harbour, Dum Dum, Durgapur, Halisahar, Haora, Hugli, Ingraj Bazar, Jalpaiguri, Kalimpong, Kamarhati, Kanchrapara, Kharagpur, Cooch Behar, Kolkata, Krishnanagar, Malda, Midnapore, Murshidabad, Nabadwip, Palashi, Panihati, Purulia, Raiganj, Santipur, Shantiniketan, Shrirampur, Siliguri, Siuri, Tamluk, Titagarh.
Cyber Forensic Expert Services in Various Major Cities of India
Mumbai | New Delhi | Bangalore | Hyderabad |
Ahmedabad | Chennai | Kolkata | Surat |
Pune | Jaipur | Lucknow | Kanpur |
Nagpur | Indore | Thane | Bhopal |
Visakhapatnam | Pimpri-Chinchwad | Patna | Vadodara |
Ghaziabad | Ludhiana | Agra | Nashik |
Meerut | Kalyan-Dombivali | Vasai-Virar | Varanasi |
Srinagar | Aurangabad | Dhanbad | Amritsar |
Navi Mumbai | Allahabad | Howrah | Ranchi |
Gwalior | Coimbatore | Vijayawada | Jodhpur |
Madurai | Raipur | Kota | Chandigarh |
Guwahati | Solapur | Hubballi-Dharwad | Nellore |
Bhavnagar | Dehradun | Durgapur | Asansol |
Rourkela | Nanded | Kolhapur | Ajmer |
Akola | Gulbarga | Mangalore | Erode |
Belgaum | Ambattur | Tirunelveli | Malegaon |
Gaya | Jalgaon | Udaipur | Maheshtala |
Davanagere | Kozhikode | Kurnool | RajpurSonarpur |
Bhatpara | Rajahmundry | Bokaro | South Dumdum |
Bellary | Patiala | Gopalpur | Agartala |
Bhagalpur | Muzaffarnagar | Ahmednagar | Mathura |
Kollam | Avadi | Kadapa | Kamarhati |
Sambalpur | Bilaspur | Shahjahanpur | Satara |
Bijapur | Rampur | Shivamogga | Chandrapur |
Junagadh | Thrissu | Alwar | Bardhaman |
Kulti | Kakinada | Nizamabad | Parbhani |
Tumkur | Khammam | Ozhukarai | Bihar Sharif |
Aurangabad | Panipat | Darbhanga | Bally |
Aizawl | Dewas | Ichalkaranji | Karnal |
Bathinda | Jalna | Eluru | KirariSuleman Nagar |
Mehsana | Durg | Barasat | Purnia |
Satna | Mau | Sonipat | Farrukhabad |
Sagar | Rourkela | Imphal | Ratlam |
Hapur | Begusarai | New Delhi | Gandhidham |
Baranagar | Tiruvottiyur | Pondicherry | Sikar |
Thoothukudi | Rewa | Mirzapur | Raichur |
Pali | Ramagundam | Haridwar | Thanjavur |
Bulandshahr | Uluberia | Murwara | Sambhal |
Singrauli | Nadiad | Secunderabad | Naihati |
Bidhan Nagar | Pallavaram | Bidar | Munger |
Panchkula | Burhanpur | Raurkela Industrial Township | Chittoor |
Jehanabad | Kharagpur | Dindigul | Gandhinagar |
Hospet | NangloiJat | Malda | Ongole |
Deoghar | Chapra | Haldia | Khandwa |
Nandyal | Chittoor | Morena | Amroha |
Anand | Bhind | Bhalswa Jahangir Pur | Raebareli |
Madhyamgram | Bhiwani | Navi Mumbai | PanvelRaigad |
Baharampur | Ambala | Morbi | Fatehpur |
Mahaboobnagar | Bhusawal | Orai | Bahraich |
Vellore | Sambalpur | Raiganj | Sirsa |
Danapur | Serampore | Sultan PurMajra | Guna |
Jaunpur | Panvel | Shivpuri | Surendranagar Dudhrej |
Kumbakonam | Dehri | Madanapalle | Phagwara |
Narasaraopet | Tadipatri | Kishanganj | Karaikudi |
Faridabad | Rajkot | Jabalpur | Tiruchirappalli |
Bareilly | Mysore | Tiruppur | Gurgaon |
Aligarh | Jalandhar | Bhubaneswar | Salem |
Mira-Bhayandar | Warangal | Jalgaon | Guntur |
Bhiwandi | Saharanpur | Gorakhpur | Bikaner |
Amravati | Noida | Jamshedpur | Bhilai |
Cuttack | Firozabad | Kochi | Jamnagar |
Ujjain | Loni | Siliguri | Jhansi |
Ulhasnagar | Jammu | Sangli-Miraj&Kupwad | Thiruvananthapuram |
Panihati | Latur | Dhule | Tirupati |
Rohtak | Korba | Bhilwara | Berhampur |
Arrah | Anantapur | Karimnagar | Etawah |
Ambarnath | North Dumdum | Bharatpur | Vijayanagaram |
Katihar | Nagercoil | Sri Ganganagar | Karawal Nagar |
Mango | Katni | Yamunanagar | Unnao |
Chinsurah | Alappuzha | Kottayam | Machilipatnam |
Shimla | Adoni | Udupi | Tenali |
Proddatur | Saharsa | Hindupur | Sasaram |
Hajipur | Bhimavaram | Siwan | Bettiah |
Guntakal | Srikakulam | Motihari | Dharmavaram |
Gudivada | Suryapet | Kavali | Tadepalligudem |
Amaravati | Buxar | Gangtok | Kolkata-West Bengal |